The Voice AI Compliance Checklist Every CX Team Should Review
Voice AI introduces regulatory complexity that many text-based AI systems do not face. This checklist covers what CX and compliance teams should review before deployment, including data residency, consent management, subprocessor disclosures and security reports.

Key highlights
Voice AI Compliance in a Nutshell
- Voice AI compliance should be reviewed across seven domains before deployment.
- These domains include consent management, data classification, call recording rules, vendor verification, security architecture, data residency, and governance processes.
- The most common compliance failure points include unclear consent mechanisms, incomplete vendor security documentation, missing subprocessor disclosures, and outbound calling rules that violate TCPA.
- Each domain should have a clear owner within the organization, typically across legal, security, engineering, and operations teams.
- Voice AI compliance continues after deployment. It requires ongoing monitoring, quarterly reviews, and continuous vendor oversight.
Voice AI compliance means checking seven domains before deployment: consent management, data classification, call recording rules, vendor verification, security architecture, data residency and governance. Each domain needs a named owner across legal, security, engineering and operations, and the review continues after go-live. Compliance remains a major barrier to deployment across contact centers, healthcare operations, financial services and customer support.
Most organizations discover compliance gaps during vendor security reviews, after the deployment plan is set. Legal teams begin asking questions about data residency, consent management, and subprocessor disclosures. Security teams request SOC 2 reports, encryption details, and access controls. Operations teams realize that call recording rules vary by region and industry.
At that stage, remediation becomes expensive and delays deployment timelines.
Voice AI introduces regulatory complexity that does not exist in many text-based AI systems. Live conversations can contain personally identifiable information, payment data, or protected health information. Voice data may also be considered biometric in certain jurisdictions.
This checklist is designed to help CX and compliance teams evaluate voice AI compliance before deployment. It organizes the most important regulatory and operational checks across seven compliance domains so legal, security, and engineering teams can review them systematically.
Used correctly, this checklist helps organizations deploy voice AI platforms with confidence while avoiding costly compliance issues later.
Short answer: On its own, no. Voice AI can enforce controls on every call, such as recording and automated-system disclosures, consent logs with timestamps, transcript redaction, role-based access and audit logs. Compliance still depends on how those controls are configured, what the vendor can document, and who in legal, security and operations owns each domain.
Why Voice AI Compliance is More Complex Than Text-Based AI
Voice AI creates a significantly larger compliance surface than text-based automation systems.
Text interactions typically process structured messages or typed queries. Voice interactions involve real-time conversations that may include sensitive information before systems have an opportunity to classify or filter the data.
Several factors increase the complexity of compliance for voice systems.
Biometric voice data considerations
In certain jurisdictions, voice characteristics can be considered biometric data. Laws such as the Illinois Biometric Information Privacy Act impose strict requirements on the collection, storage, and use of biometric identifiers.
Organizations must evaluate whether voice recordings or voiceprints fall under biometric regulation.
Real-time data exposure
During live calls, customers may share personal information such as addresses, account numbers, or health information. Systems must handle these disclosures securely in real time.
This requires encryption, access controls, and proper mechanisms for redacting transcripts.
Jurisdiction-based call recording rules
Call recording regulations differ by location.
Some jurisdictions allow recording with one-party consent. Others require explicit consent from all parties before recording begins.
Organizations operating across multiple regions must configure recording disclosures based on caller location.
Consent disclosure requirements
Some rules require callers to be told that they are interacting with an automated system. Article 50 of the EU AI Act applies this duty from August 2, 2026.
Where a disclosure is required, give it at the start of the conversation and keep a record of it for audits.
Because voice interactions occur in real time and span multiple regulatory environments, compliance must be built into the system's architecture from the start.
Compliance and governance frameworks are also closely linked to operational performance metrics, such as first-call resolution rates (opens in a new tab) and call containment.
Understanding these metrics helps organizations evaluate the real impact of automation deployments.
The Regulatory Picture in 2026
Voice AI deployments must navigate several regulatory frameworks. The most relevant regulations depend on industry, geography, and the type of data processed during conversations.
Below are the most common security frameworks CX teams encounter when deploying voice AI (opens in a new tab).
GDPR
The General Data Protection Regulation governs the processing of personal data of individuals in the European Union.
Voice AI systems must comply with the GDPR when processing personal data of people in the EU.
Key requirements include a lawful basis for recording and processing calls (consent is one of several), the ability for individuals to request deletion of their data, and transparency around data processing activities.
Organizations must also conduct Data Protection Impact Assessments when deploying high-risk systems.
Penalties can reach €20 million or 4 percent of worldwide annual turnover, whichever is higher.
HIPAA
The Health Insurance Portability and Accountability Act applies when voice AI systems process protected health information.
Healthcare providers, insurers, and service vendors must sign Business Associate Agreements with any technology vendor that handles PHI.
Voice AI platforms must implement administrative, technical, and physical safeguards to protect healthcare data.
As of October 2026, the inflation-adjusted HIPAA civil money penalties in 45 CFR 102.3 (opens in a new tab) range from $145 to $2,190,294 per violation, with a calendar-year cap of $2,190,294 for identical violations.
TCPA
The Telephone Consumer Protection Act regulates automated outbound calling in the United States.
Organizations using AI to initiate outbound calls must obtain prior consent and comply with the 'Do Not Call registry' requirements.
TCPA rules apply differently to inbound and outbound interactions.
Statutory damages are $500 per violation, and a court can triple them to $1,500 when the violation is willful or knowing.
EU AI Act
The European Union AI Act introduces a risk-based classification system for AI systems.
Most customer service voice AI deployments carry the transparency duties for limited-risk systems. A few uses, such as creditworthiness checks or risk pricing for life and health insurance, are high-risk.
High-risk systems must meet additional transparency, governance, and monitoring requirements.
As of October 2026, the Digital Omnibus on AI, Regulation (EU) 2026/1744 (opens in a new tab), sets the high-risk obligations to apply from December 2, 2027 for Annex III systems and from August 2, 2028 for systems covered by Annex I.
Penalties reach €15 million or 3 percent of worldwide annual turnover for most breaches, and up to €35 million or 7 percent for prohibited practices, whichever amount is higher.
CCPA, CPRA, and US state regulations
The United States does not have a single federal AI regulation.
Instead, organizations must navigate a growing patchwork of state laws such as the California Consumer Privacy Act and Colorado's automated decision-making law (SB26-189), whose main obligations start January 1, 2027.
These laws grant consumers rights related to data access, deletion, and opt-out requests.
Some states also impose rules around automated decision systems.
PCI DSS
The Payment Card Industry Data Security Standard applies when voice AI systems handle cardholder data.
Organizations must ensure payment information is protected during calls.
Security practices such as DTMF masking and pause-and-resume recording are commonly used when payment data is entered.
Failure to comply can result in financial penalties and loss of payment processing privileges.
Evaluating voice AI vendors for compliance readiness? Explore how Orvera supports vendor security reviews with structured governance controls and transparent compliance documentation. (opens in a new tab)(same text, styled h2)
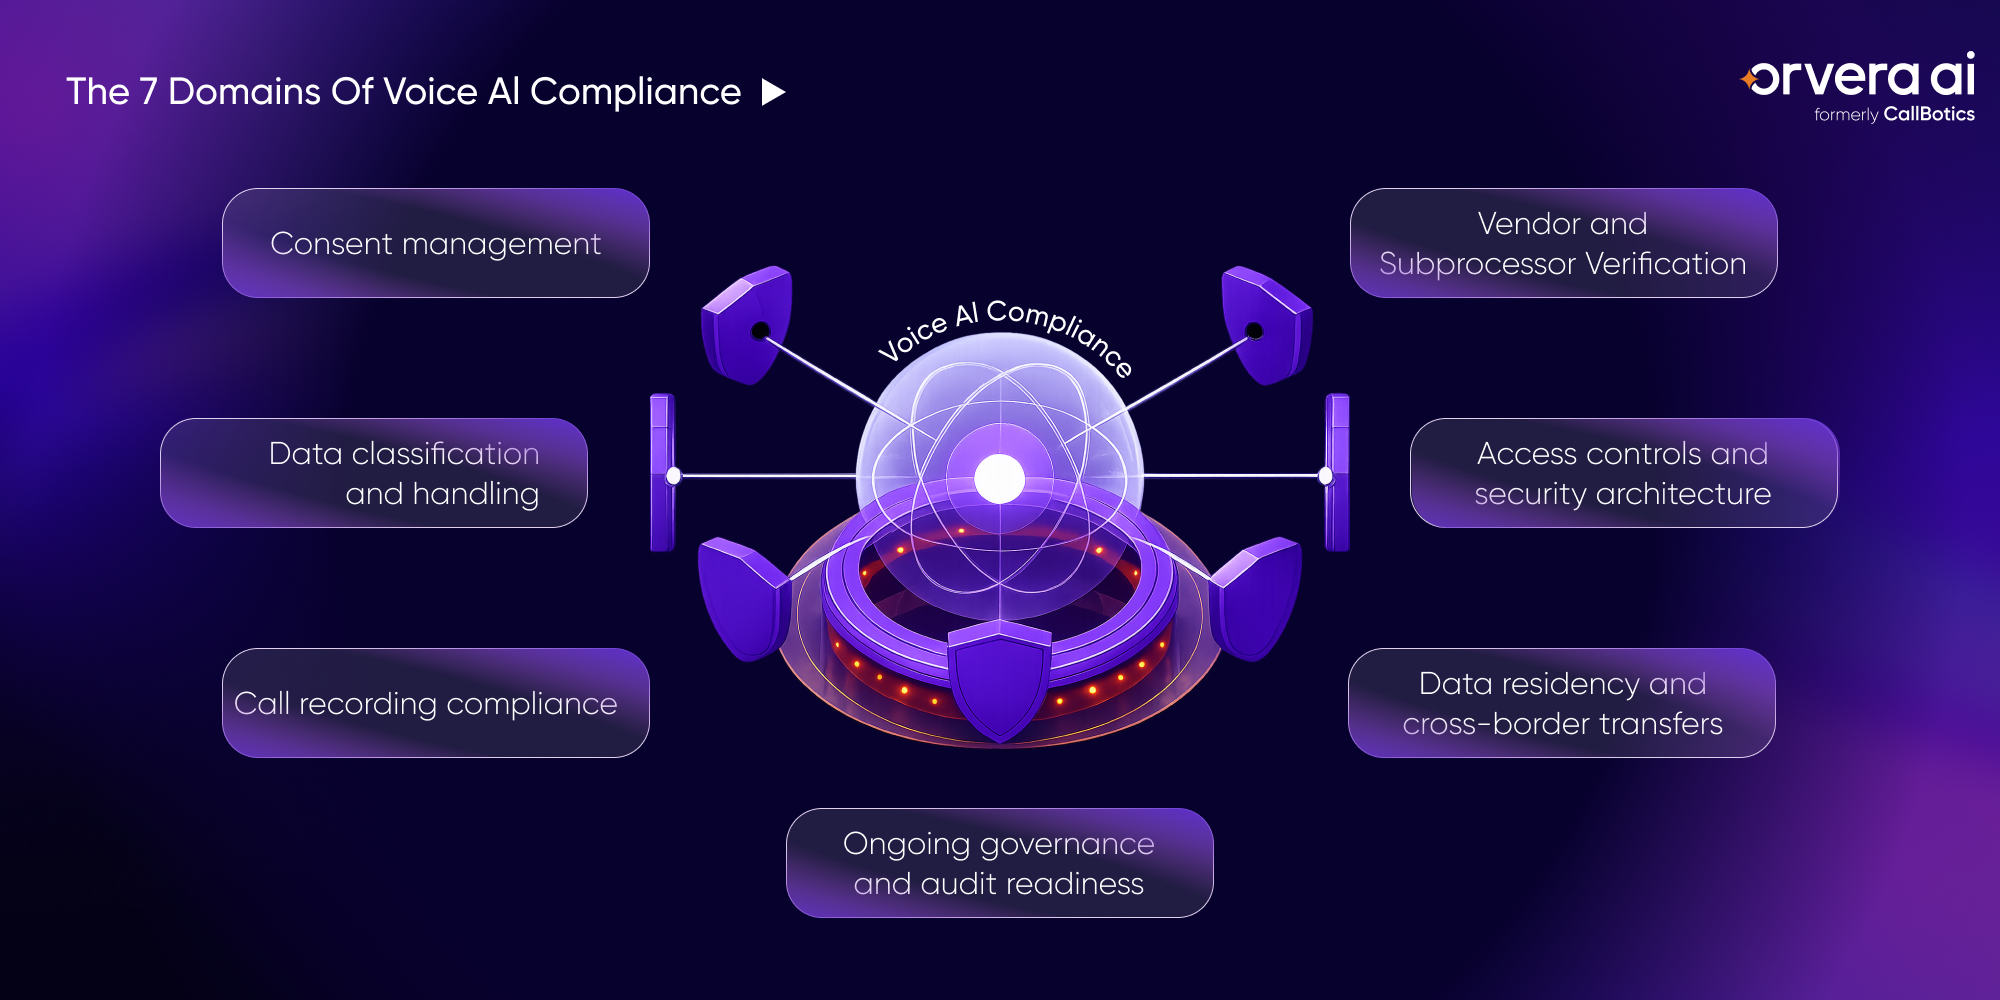
Voice AI deployments should be reviewed across seven compliance domains.
Each domain represents a critical control area that legal, security, and engineering teams must evaluate before deployment.
Domain 1 Consent management
Organizations must verify that callers provide explicit consent when required by regulation.
Consent should include disclosure that the call may be recorded and that the caller is interacting with an automated system.
Consent mechanisms should be specific to the purpose of the interaction. Systems should log consent with timestamps to enable organizations to demonstrate compliance during audits. Ownership typically sits with legal and compliance teams.
Domain 2 Data classification and handling
Voice interactions may contain several types of sensitive data, including personally identifiable information, protected health information, and payment details.
Organizations should classify data types and implement policies that govern how each category is processed and stored. Encryption should be enforced both during transmission and when data is stored. Transcripts should include automated redaction mechanisms for sensitive information.
Data retention and deletion policies should be clearly defined. Security and engineering teams typically own this domain.
Domain 3 Call recording compliance
Recording rules vary by jurisdiction.
Systems should be able to configure recording disclosures based on caller location and applicable law. Organizations must ensure callers receive appropriate notifications before recording begins. Compliance checks should also include storage policies for recorded calls and transcripts.
Legal and operations teams typically manage this domain.
Domain 4 Vendor and Subprocessors Verification
Procurement teams should verify the security posture of any voice AI vendor before signing contracts.
Organizations should request the vendor's SOC 2 Type II report and read it. Healthcare deployments should confirm the availability of Business Associate Agreements. Data processing agreements should clearly list subprocessors and data handling responsibilities.
Vendor risk management and security teams typically own this review.
Domain 5 Access controls and security architecture
Voice AI platforms must implement strong security controls.
These controls include role-based access permissions, multi-factor authentication, and centralized identity management. Audit logs should track user activity across the system. Incident response procedures should be documented and tested.
Voice automation platforms also connect directly to operational systems, such as CRM platforms, enabling customer conversations to trigger workflows automatically. Security and engineering teams typically manage these safeguards.
Domain 6 Data residency and cross-border transfers
Data residency requirements can affect organizations operating in multiple regions. Certain jurisdictions require customer data to remain within specific geographic boundaries.
CX teams should confirm that vendors can process and store data in approved regions. Contracts should clearly define where data is stored and processed. Legal and compliance teams typically oversee this domain.
Domain 7 Ongoing governance and audit readiness
Compliance does not end once a system is deployed.
Organizations should schedule regular reviews of AI systems to ensure ongoing compliance with regulatory requirements. Responsibilities should be assigned across legal, security, engineering, and operations teams.
Audit preparation should include documentation of vendor certifications, data flows, and security controls. Governance teams typically oversee these processes.
Industry-Specific Compliance Priorities
While the core compliance framework remains consistent, regulatory priorities vary across industries (opens in a new tab).
Healthcare
Healthcare deployments must prioritize HIPAA compliance and the protection of PHI.
Organizations should ensure that transcripts automatically redact sensitive medical information.
Vendor contracts should include Business Associate Agreements that extend to any language-model subprocessor, and zero-retention terms where possible.
Testing should include real-world conversation scenarios to identify potential PHI exposure.
Financial services
Financial institutions must comply with PCI DSS when processing payment information during calls.
Audit trails are also important for supervisory review of customer interactions.
SOC 2 Type II certification is commonly required during vendor procurement.
BPO and contact centers
BPO environments must support multiple clients across different regulatory environments.
Platforms should support jurisdiction-based recording rules and consent mechanisms.
Outbound campaigns must comply with TCPA and Do Not Call registry requirements.
Client-specific data handling agreements are also common.
Telecommunications
Telecom operators may handle subscriber voice data at the network level.
This creates additional regulatory requirements related to data access and subscriber privacy.
Systems embedded within telecom infrastructure must also comply with national telecommunications regulations.
The Most Common Compliance Gaps CX Teams Miss
Many organizations encounter similar issues during vendor security reviews.
One of the most common problems is bundled consent. Some systems rely on general terms of service for call recording or automated interaction consent.
Another common issue is vendors displaying a SOC 2 certification badge without providing the actual SOC 2 Type II report.
Organizations may also overlook subcontractor disclosures, particularly when vendors rely on external AI providers.
Outbound calling compliance is another frequent failure point. Some systems initiate automated calls without verifying Do Not Call registry requirements.
Identifying these issues early helps organizations avoid compliance risks later.
How to Evaluate a Voice AI Vendor’s Compliance Posture
CX teams should follow a structured process when evaluating voice AI vendors.
First, request the vendor’s SOC 2 Type II report and review its scope.
Second, verify whether the vendor supports industry-specific agreements such as HIPAA Business Associate Agreements.
Third, review the vendor’s data processing agreement to confirm all subprocessors are disclosed.
Fourth, confirm the vendor’s data residency options align with regulatory requirements.
Finally, evaluate whether the platform supports consent management, access controls, and audit logging.
This structured evaluation process reduces the risk of deploying systems that fail security or compliance reviews.
Before deploying voice automation, ensure your platform meets your compliance standards. See how Orvera AI is designed to support consent management, audit visibility, and secure integrations across your existing stack. (opens in a new tab)How Orvera Is Built for Compliance
Voice AI deployments require governance, auditability, and operational transparency built into the platform from day one. Orvera delivers AI agents for customer experience teams, built, deployed and run by teams with 18+ years of contact-center experience, and its architecture reflects the real compliance requirements that regulated customer operations face. From data governance and access control to audit visibility and operational monitoring, the platform is structured to help organizations deploy voice automation while maintaining the security, accountability, and compliance oversight regulated operations require.
How the platform supports compliance teams
- SOC 2 Type II certified security architecture: Designed for regulated environments with secure data handling practices, role-based access control, and structured governance policies.
- Full interaction audit visibility: Built-in monitoring and audit trails allow organizations to review conversations, track system actions, and maintain operational transparency.
- Consent and compliance management: Supports consent handling and regulatory communication requirements commonly required in customer-facing voice environments.
- Native quality monitoring and compliance oversight: Automated QA and interaction monitoring help organizations maintain consistent service quality and regulatory adherence.
- Direct integration with business systems: Connects directly with CRM, CCaaS, and operational systems while maintaining governance and access controls.
- White-glove implementation and support: Every deployment is guided by implementation specialists to ensure security, compliance, and operational readiness from the start.
- Operator-built workflow architecture: Designed by teams with deep contact center experience, ensuring automation workflows reflect real escalation paths and compliance requirements.
- Structured deployment, end to end: Security documentation is available to procurement teams on request for vendor reviews.
Conclusion
Compliance in voice AI deployment is ongoing work.
It requires continuous monitoring, governance, and vendor oversight.
CX teams should treat this checklist as both a pre-deployment review and an ongoing audit framework.
By assigning ownership across legal, security, engineering, and operations teams, organizations can deploy voice AI systems confidently while maintaining regulatory compliance.
Voice AI can deliver significant operational value, but only when compliance is designed into the system from the start.
Frequently asked questions
The most common frameworks include GDPR, HIPAA, TCPA, PCI DSS, the EU AI Act, and several US state privacy regulations.
Yes, if the system processes protected health information in healthcare environments.
SOC 2 Type I evaluates security controls at a single point in time. SOC 2 Type II evaluates how those controls operate over a longer period.
Organizations must obtain consent before initiating automated calls and must comply with the Do Not Call registry rules.
Organizations should review subprocessor disclosures, data residency commitments, data retention policies, and security safeguards.
Build the checks into the call flow. Play the recording and automated-system disclosures at the start of each call based on the caller's location, log consent with a timestamp, redact sensitive details from transcripts automatically, and enforce role-based access and audit logs. Legal, security and operations owners then review those logs on a regular schedule.
Written by
Anindita Majumder
Anindita Majumder is a communications professional with nearly four years of experience in public relations, corporate communications, and journalism. She creates content that helps brands communicate their vision, products, and expertise through press releases, thought leadership, and editorial pieces. Outside of work, she is a vocalist, which keeps her creativity flowing.